AWS IAM
AWSCloudIAMSecurityaccess control
- >It's a global service.
- >The root account is created by default — it shouldn't be shared or used.
- >If we're not going to use it, what then? Create users.
Users
- >Users can be grouped.
- >A group can contain users but not other groups.
- >Users don't need to be in a group.
- >One user can be in multiple groups.
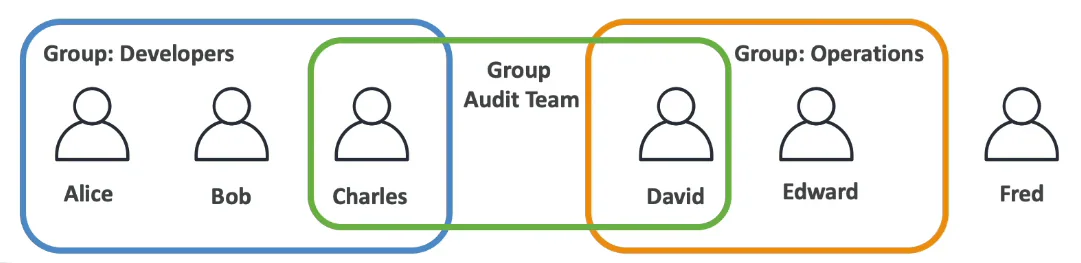
Expand
IAM policies
Users and groups can be assigned JSON documents, i.e. policies.
code
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": "s3:ListBucket",
      "Resource": "arn:aws:s3:::example-bucket"
    }
  ]
}
IAM recall4 blanks
IAM is a service. Groups can contain users but not other , and a user may belong to groups. Permissions are attached as policy documents.
try it before revealing