Suhesh Kasti
Exploring application security, network infrastructure and application delivery. Here documented are braindumps of all my learnings, exploration and mistakes as well.
About Me
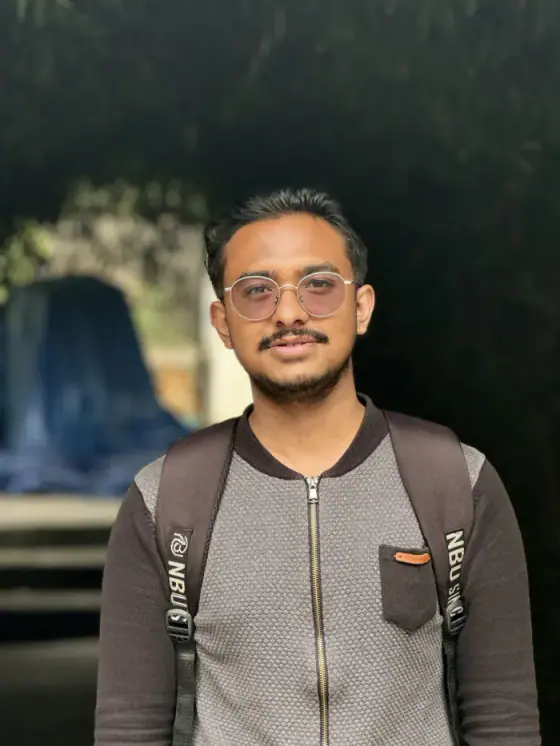
Suhesh Kasti
Application Security Engineer & Offensive Security
I'm an application security engineer. I secure applications from notorious hacker people. Right now, I'm learning offensive security and pentesting. You either die a defender or live long enough to become an attacker.
This site is my brain dump — raw, unfiltered research notes, project writeups, and weird experiments.
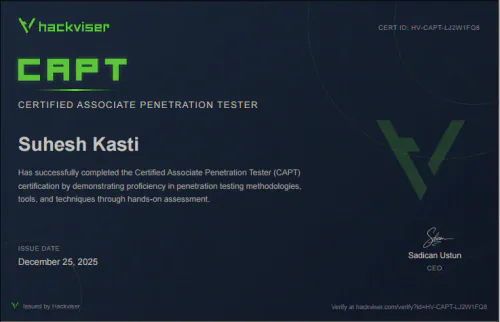
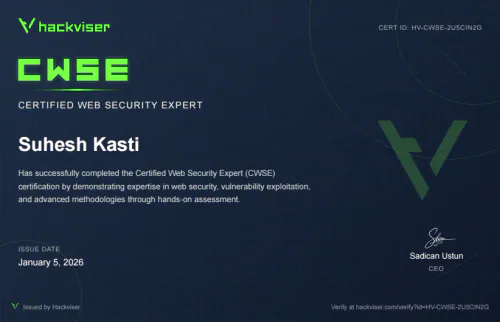
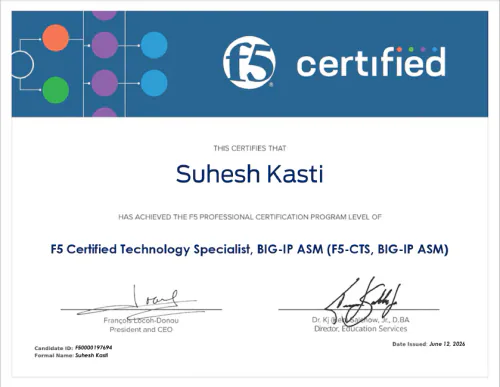
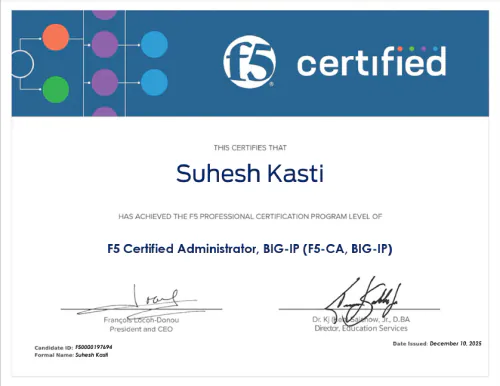
Education & Qualifications
Bachelors
Computer Science & Information Technology — Nepalaya College
Higher Education
Gyankunj HSS & College
Experience Timeline
Application Security Engineer
Digital Network Solutions
Protect client web applications against layer 7 attacks using WAF. Strengthen security posture through vulnerability assessments, configuration audits, and WAF tuning.
- Protect client's web applications against various layer 7 attacks
- Help clients strengthen their security posture
- Configure and maintain Web Application Firewalls
Associate Security Research Analyst
SecurityPal Inc.
Enhanced clients' digital security through handling security questionnaires and knowledge base enrichment. Analyzed compliance requirements.
- Enhance the client's knowledge repository
- Respond to prospect's security questionnaires
- Analyze and document security compliance requirements
Technical Support Representative
Subisu Cablenet Ltd.
Transformed digital challenges into seamless connectivity. Managed network setup, remote diagnostics, and customer technical support at a major ISP.
- Assist with network setup and configuration
- Conduct remote diagnostics, support, and configurations
- Manage end-user connectivity and technical issues
Skills
- Web Exploitationlabs + CAPT / CWSE
- Burp Suitemy main testing tool
- API SecurityREST, auth, Postman
- PortSwigger Academy95 written up, more pending
- Network Testingnmap, metasploit, labs
- Recon & OSINTtooling I built myself
- Security Research3 months · SecurityPal
- HTB CPTSstudying now
- Mobile Pentestinglearning on the side
BIG-IP & Delivery
- F5 ASM / AWAF — 2.5 yrs · production
- WAF Policy Tuning — daily, false positives included
- LTM Load Balancing — pools and virtual servers
- F5 DNS / GTM — working knowledge
- SSL/TLS — offload, profiles, certs
- Traffic Analysis — logs, tcpdump, Wireshark
- Health Monitors — tuning, not just adding
- Troubleshooting — SSL, DNS, routing, pressure
- Log Analysis — from noise to root cause
IT & Network Admin
- Linux — 3 yrs · RHEL, Debian, Arch
- Networking — TCP/IP, NAT, VLANs
- DNS & BIND — zones, records, DNSSEC
- Windows / WSL — daily at work
- Packet Capture — Wireshark, tcpdump
- Remote Diagnostics — customer CPE and routers
- Hardware — modems, switches, cabling
- Connectivity — line faults and link issues
- VPNs — remote access and tunnels
DevOps & Automation
- Docker — daily · comfortable, not an expert
- Git & GitHub — daily
- Bash — daily shell work
- Python — scripts and automation
- REST APIs — curl, Postman, JSON
- Virtualization — VMware, KVM, Proxmox
- NGINX — config and troubleshooting
- ELK Stack — deployed it for logs
- Deployment — built and shipped this site
Clients & Communication
- Customer Support — 3+ yrs · ISP to enterprise
- De-escalation — annoyed callers, kept calm
- Ticket Triage — SLAs, priorities, escalations
- Plain-English Security — explaining a blocked request
- Cross-Team Work — app teams and clients
- Documentation — runbooks and clean notes
- Remote Sessions — talking people through fixes
- Training — built an app to train recruits
- Questionnaires — vendor and compliance work
Building a Local AI-Powered Security Research Agent from Scratch
A full honest build log of setting up a completely local, private AI agent stack for authorized security research and bug bounty — llama.cpp, Goose, Qdrant RAG, model routing, Telegram integration — everything that went wrong and how it got fixed.
Locking Down Ports on F5 BIG-IP
Port lockdown on a self IP decides which management ports answer on that interface — the switch between reaching the BIG-IP and leaving it exposed.
Configuring DNSSEC on F5 BIG-IP DNS
A step-through for signing a zone with DNSSEC on BIG-IP DNS — generating the ZSK and KSK, creating the zone, and building the chain of trust.
Wireshark Basics
Conversation filters, profiles, custom time columns and colouring rules — the Wireshark setup tweaks that make packet analysis less painful.
TryHackMe — Basic Pentesting
A TryHackMe Basic Pentesting room: SMB enumeration exposes a staff list, a private key cracks under john, and a backup file hands over the root password.
Featured Work
Local AI Security Agent
Two local models, a RAG index I keep fed with live CVE data, MCP tools for nmap and search, and a Telegram bot so I can ask it things from my phone. Nothing leaves the GPU.
Security Writeups
Every lab and box I have worked through, written up the way I wish someone had explained them to me. The payloads, the dead ends, and the parts I got wrong first.
RemarkEnks
A browser extension that writes TSC remarks for Subisu operators. One click instead of the usual copy-paste routine, and it saved the team a serious number of hours.
Re-Earth Waste Management
Frontend work on a waste management platform in Nepal. I built the interface while the rest of the team handled the backend.